

Belgium 01-10-2026 Squad Only Virtual english
Low-code, no-code, and AI tools are giving business teams more ability to build solutions themselves. The challenge is setting the right boundaries before fast local solutions become important operational assets. Three pressure points need attention. - Boundaries must be clear: teams need to know what they can build alone and what requires IT, security, or architecture review. - Supportability matters when a quick solution becomes business-critical. - Risk control remains necessary around data access, compliance, security, process dependency, and maintenance. The working question is simple: how do we enable business-led development while keeping security, ownership, and support under control? If you are trying to enable this safely, let’s compare approaches with others facing the same balance.
Read More
Belgium 06-10-2026 All Members Physical english
As enterprise AI transitions from experimental Proofs of Concept (POCs) into real implementations, digital leaders are encountering a shared challenge: consumption-based public cloud token billing models do not fit neatly into traditional IT budgeting. Daily token consumption can rise unexpectedly, pushing expenses through the roof while arbitrary caps quickly kill momentum for innovation. For many CIOs, this raises an open strategic question: How do we keep costs under control while further stimulating innovation? During this interactive CIONET roundtable, we will explore among peers how to navigate AI tokenomics. Rather than treating public cloud LLMs as the default path, we will investigate how different execution environments, ranging from hybrid cloud setups and targeted on-premise models to specialised edge hardware, can help balance cost with performance. This session is intentionally designed as an open peer-to-peer exchange; a space to compare notes, challenge current ways of working and architectural setups, and discuss practical approaches to building predictable, scalable AI models.
Read More
Belgium 08-10-2026 All Members Physical english
Every large organisation has been through a major transformation, and most through several. The word transformation is misleading because it suggests a beginning and an end. But organisations that do well are the ones that have given up on the idea of arriving and realise that constant change has become the new norm, and missing a single cycle leaves you permanently behind. This evening, two leaders will share how they think about this, coming from opposite directions. John Porter led Telenet through a sustained period of reinvention spanning the pandemic, a full reorganisation into tribes, M&A, and a shift to a performance driven culture. Along the way, the IT department was dissolved and technology was embedded inside autonomous tribes that run as small businesses. There is no CIO at Telenet. It is Telenet Group’s purpose to become a digital-first, customer-centric organisation. To deliver on this ambition, it has embarked on a transformation journey built on three pillars: (i) the implementation of a scaled-agile operating model (organisation), (ii) the acceleration of digitisation and automation underpinned by optimised IT systems, platforms, and strategic technology partnerships (digitisation), and (iii) a performance leadership culture focused on accountability, ownership, and a change mindset (culture). Kris Vervaet, on the other hand, has just become CIO at KBC, the bank whose mobile app has been ranked best in the world three times and whose AI assistant Kate now handles 70% of customer queries on its own. But Kris is no ordinary CIO: he ran DPG Media Belgium as CEO, and KBC went looking for someone who has led transformation rather than someone who manages technology. So while one organisation got rid of the CIO role, the other reinvented it, and both are thriving. The conversation will range across organisational and IT redesign, the rise of digital-first customer experience, the impact of AI on how every business is run, and the harder questions of culture, talent and leadership. The question for every leader in the room is what that tells you about your own role, your own operating model, and the pace at which you are prepared to keep evolving.
Read More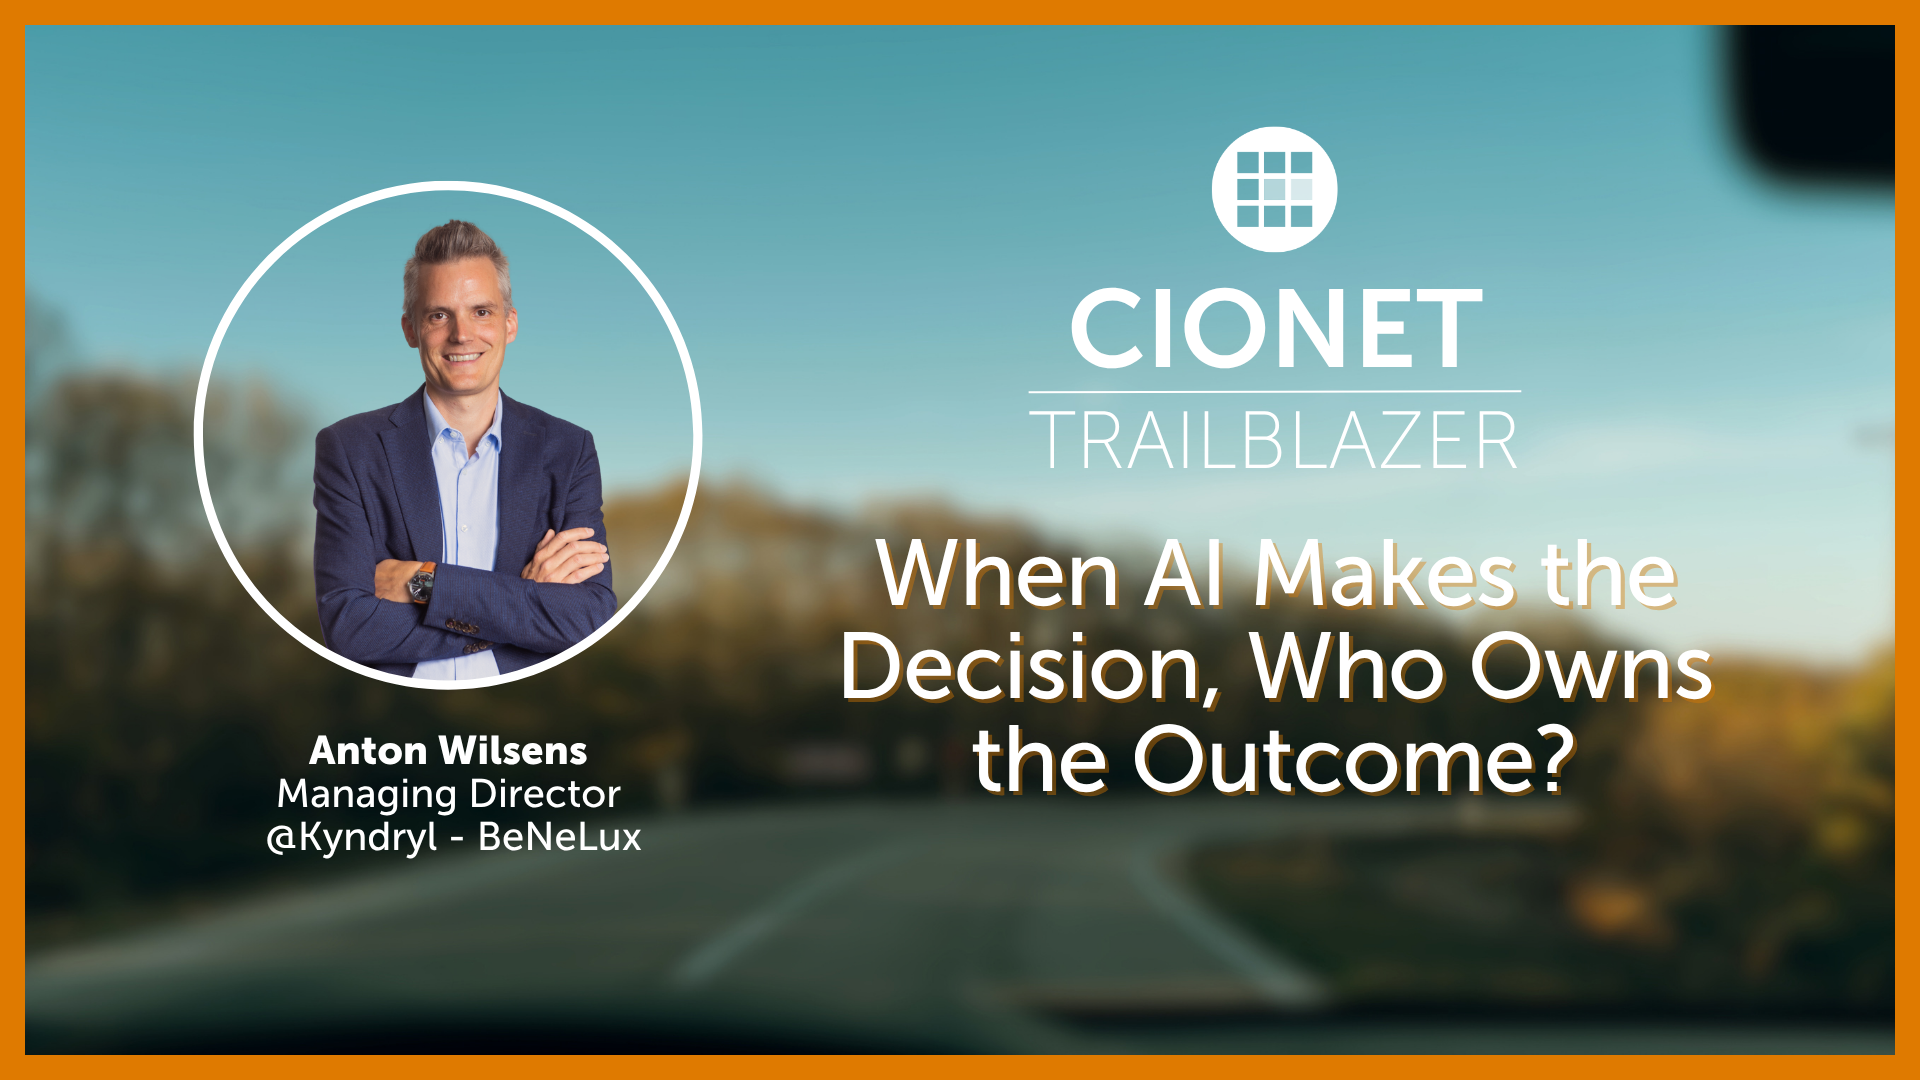
Published on: September 30, 2026 @ 1:17 PM
Published on: August 26, 2026 @ 9:13 AM
Published on: July 29, 2026 @ 10:08 AM
Published on: June 24, 2026 @ 5:00 PM
Published on: May 27, 2026 @ 9:21 AM
Published on: May 07, 2026 @ 4:02 PM

Published on: April 29, 2026 @ 9:11 AM
Published on: March 26, 2026 @ 3:37 PM

Published on: March 25, 2026 @ 9:58 AM
Published on: March 13, 2026 @ 3:43 PM

Published on: February 25, 2026 @ 11:01 AM

Published on: February 25, 2026 @ 9:00 AM
Published on: February 24, 2026 @ 5:00 PM
CIONET Trailblazer: CISO: The Shift from Prevention to Resilience: Turning Visibility into Execution
Published on: January 28, 2026 @ 9:48 AM
CIONET Trailblazer: AI Transformation: Bridging the Cultural Divide to Achieve Competitive Advantage
Published on: December 17, 2025 @ 9:16 AM
Published on: October 29, 2025 @ 11:31 AM
Published on: July 30, 2025 @ 9:19 AM
Published on: June 25, 2025 @ 9:14 AM

Published on: April 30, 2025 @ 9:04 AM

Published on: March 26, 2025 @ 9:59 AM

Published on: March 04, 2025 @ 5:07 PM
Published on: February 26, 2025 @ 10:51 AM
Published on: February 25, 2025 @ 4:14 PM

Published on: February 25, 2025 @ 10:33 AM
Published on: January 29, 2025 @ 9:58 AM
Published on: December 18, 2024 @ 9:07 AM
Published on: October 30, 2024 @ 9:34 AM

Published on: October 29, 2024 @ 11:37 AM

Published on: September 27, 2024 @ 10:41 AM
Published on: September 25, 2024 @ 8:59 AM
Published on: September 18, 2024 @ 3:44 PM
Published on: August 28, 2024 @ 10:10 AM
Trend Micro reduced the time spent investigating false positives by 75 percent.
Trend Micro reduced the time spent investigating false positives by 75 percent.
WHAT IS OUR PRIMARY USE CASE?
We use Trend Vision One™ for antivirus, endpoint protection, and identifying misconfigurations in our cloud platform. It secures our servers and endpoints and detects any sort of malicious software or inappropriate user behavior. It's a cloud solution with agents on the machines for endpoint protection.
Migrating to the Trend Vision One platform helped us because we no longer need to look at eight different screens to find data. It's all just consolidated into one location. Having everything in one place is critical. I've been in the industry for almost a decade now, and it's a struggle to find that single pane of glass for all my alerts, logs, and anomalies like random users clicking on a link or downloading a file.
HOW HAS IT HELPED MY ORGANIZATION?
Trend Vision One gives us more insight. When we implemented the solution, we didn't have a mature security platform, so we couldn't see what was happening on our servers or what our users were doing. It has decreased our time to detect and respond. Initially, we didn't have as much insight into any attacks that came through.
It gives us more data points to work with and guidance about the remediation efforts. We aren't dealing with eight or nine different systems to identify one issue. It's all centrally located in one place.
Trend Micro™ Managed XDR acts as our security operations center. It helps us sleep a little better at night. We know that they can call us on the phone when a significant alert comes in after hours. It makes things more efficient because we know there's someone on the other side who can look at alerts for us and at least do the preliminary analysis if anything comes in.
Multiple teams are notified when an alert comes in. We can allocate security resources more efficiently and plug more data sources into the Trend Vision One platform. We don't need to dedicate personnel to continuously monitor the dashboard because we know someone is looking at it with us.
The platform has allowed us to identify blind spots and see where there are holes in our network. It suggests remediation steps in many cases. There is typically a link in the documentation. That has been a significant benefit because it tells you what to do. For example, it might suggest running a command in the terminal to identify the issues or take x output and put it into y input.
The solution reduces the time spent investigating false positives by around 65 to 75 percent. For example, when we are pushing out custom code, the workbench tells us the risk level. If it's 70 or higher, we check it out. At 69 or lower, it could be a false positive, so it might require some poking around. It gives us enough data in the alerts that anyone who knows the system could say, "Oh, that was me. I was running patches," instead of checking nine different systems to identify what triggered the alert. It's all there in the alert, including the hashes, commands, impacted web files, etc. We can instantly dismiss it as a false positive and flag it as resolved.
Trend Vision One's playbooks help us save time but I can't say how much because we're still maturing those. For instance, we know what those patching commands look like, so we're working on a playbook to automatically ignore or close those false positive alerts as they come in. We're still trying to fine-tune those playbooks.
WHAT IS MOST VALUABLE?
I like Trend Vision One's observed attack techniques feature. It lets you see what an attacker is doing, how they have tried to exploit a machine, or how malicious code is operating. It helps us discover indicators of compromise so we can write better rules for detection.
Migrating to the Trend Vision One platform helped us because we no longer need to look at eight different screens to find data. It's all just consolidated into one location. Having everything in one place is critical. I've been in the industry for almost a decade now, and it's a struggle to find that single pane of glass for all my alerts, logs, and anomalies like random users clicking on a link or downloading a file. It's nice to have it all in one location. Having centralized visibility saves the time we would spend checking various systems to look for things. I can also correlate data points more effectively and make data-driven decisions about the remediation and mitigation of any internal or external threats discovered.
The executive dashboard is nice. It's consolidating all of the tools into the Trend Vision One platform, giving you a high-level overview. Executives love dashboards and pretty colors. The ability to drill down into XDR detection from the executive dashboard his handy. I don't have to go fishing. We get an alert that says a machine did X, and I can fire it up. It's on the dashboard, so I can click on that machine, and it lets me drill down into the logs. It cuts down on the time required to do any kind of forensic analysis on anomalous alerts or behavior.
The Risk Index gives you an overview of the risk and how it compares with others in your industry. It's nice to be able to quantify the risk, and it enables you to justify the spending on these tools to your executives by showing that it pays off. Also, if we start plugging in more data points and the risk score goes up, we can conclude that there are some issues with the new data source that we just hooked up to our platform. The goal is to have a risk level of zero, but that will be hard to achieve.
Having centralized visibility saves the time we would spend checking various systems to look for things. I can also correlate data points more effectively and make data-driven decisions about the remediation and mitigation of any internal or external threats discovered.
WHAT NEEDS IMPROVEMENT?
We've received some mild complaints that the documentation is sometimes not up to date.
FOR HOW LONG HAVE I USED THE SOLUTION?
I used Trend Vision One at my last job, and I brought them on board when I joined this company, so I have been using the platform for about two years.
WHAT DO I THINK ABOUT THE STABILITY OF THE SOLUTION?
I haven't had any issues with stability.
WHAT DO I THINK ABOUT THE SCALABILITY OF THE SOLUTION?
We run several different AWS accounts, and Trend Vision One keeps up pretty well. I haven't noticed any downtime, lagging, or crashes.
WHICH SOLUTION DID I USE PREVIOUSLY AND WHY DID I SWITCH?
They were using something else, but my team wasn't in charge of it. Trend Vision One offers a more mature platform. I had used it at my previous job. My boss brought it in because we had both worked with Trend Micro in the past. We know the platform and the engineers.
HOW WAS THE INITIAL SETUP?
Deploying Trend Vision One was relatively straightforward. We were on the legacy platform. They had written a script, so all you had to do was hit the play button. We recently moved to their all-in-one Trend Vision One platform, which was super simple. The deployment team included two on our side and two on the Trend Micro side. Their engineers hopped on a call and walked us through the process. The setup process primarily entails deploying the agents globally.
WHAT'S MY EXPERIENCE WITH PRICING, SETUP COST, AND LICENSING?
Trend Micro's licensing is fair.
WHAT OTHER ADVICE DO I HAVE?
I rate Trend Micro nine out of 10. This is a SaaS product, so you can do a trial period. If you like it, contact their sales people and try to develop a good relationship with the company.
WHICH DEPLOYMENT MODEL ARE YOU USING FOR THIS SOLUTION?
Public Cloud.
CIONET’s Cyber Circle: a new three-event programme exclusively focusing on the most urgent, complex, and high-impact challenges in cybersecurity today. Launched in 2026, this initiative brings together CISOs, CIOs, and senior IT executives with a strong interest in cybersecurity for three curated gatherings each year. As part of CIONET’s trusted executive community, the Cyber Circle provides a confidential, peer-driven environment to exchange insights, share real-world experiences, and address evolving cyber threats. Each session is designed to foster strategic dialogue, strengthen resilience, and elevate cybersecurity as a core driver of business value.
Read More
The Telenet Business Leadership Circle powered by CIONET, offers a platform where IT executives and thought leaders can meet to inspire each other and share best practices. We want to be a facilitator who helps you optimise the performance of your IT function and your business by embracing the endless opportunities that digital change brings.
Read More
Découvrez la dynamique du leadership numérique aux Rencontres de CIONET, le programme francophone exclusif de CIONET pour les leaders numériques en Belgique, rendu possible grâce au soutien et à l'engagement de nos partenaires de programme : Deloitte, Denodo et Red Hat. Rejoignez trois événements inspirants par an à Liège, Namur et en Brabant Wallon, où des CIOs et des experts numériques francophones de premier plan partagent leurs perspectives et expériences sur des thèmes d'affaires et de IT actuels. Laissez-vous inspirer et apprenez des meilleurs du secteur lors de sessions captivantes conçues spécialement pour soutenir et enrichir votre rôle en tant que CIO pair. Ne manquez pas cette opportunité de faire partie d'un réseau exceptionnel d'innovateurs numériques !
Read More
CIONET is committed to highlighting and celebrating female role models in IT, Tech & Digital, creating a leadership programme that empowers and elevates women within the tech industry. This initiative is dedicated to showcasing the achievements and successes of leading women, fostering an environment where female role models are recognised, and their contributions can ignite progress and inspire the next generation of women in IT. Our mission is to shine the spotlight a little brighter on female role models in IT, Tech & Digital, and to empower each other through this inner network community.
Read More